Stop taking manual screenshots of pull requests for your auditor
EvidenceLog automatically snapshots peer review approvals, test runs, and commit SHAs directly inside Jira when issues move to Done. Tamper-evident proof for SOC 2 CC8.1, ISO 27001, and APRA CPS 234—with zero spreadsheet tax.
Built natively for Atlassian Jira Cloud & your modern developer stack
HOW IT WORKS
Zero forms. Zero audit fire drills. 3 steps.
Your team keeps shipping code in GitHub, GitLab, or Bitbucket. EvidenceLog handles the audit trail automatically.
Write code and review PRs normally
Engineers open pull requests, run CI tests, and approve code inside GitHub, GitLab, or Bitbucket as usual. Zero forms, zero compliance checklists, and zero disruption to daily engineering velocity.
Move Jira ticket to Done — EvidenceLog locks the proof
Export a signed audit pack in 5 seconds
EVIDENCELOG MAKES AUDIT READINESS FAST & EFFORTLESS
Experience continuous change compliance sealed in Jira
Block unreviewed code before it hits main
Enforce segregation of duties directly in Jira. If the author tries to self-approve or close a ticket without review, the transition is blocked.
- Enforces Author ≠ Approver on every merge
- Zero unreviewed code reaches production
Automated PR, QA & Security Verification
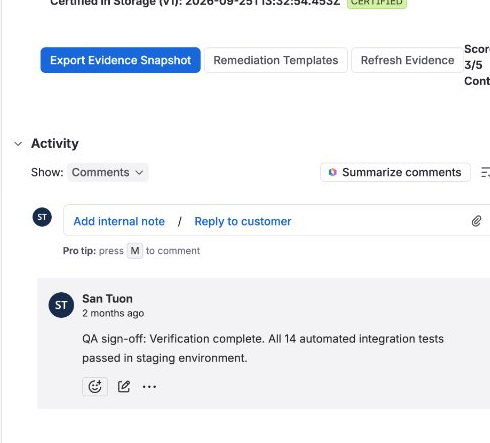
Real-time verification of acceptance criteria, git links, independent peer reviews, QA sign-offs, and automated security scans.
- Auto-detects GitHub, GitLab & Bitbucket links
- Snyk, SonarQube & Trivy scan detection
Actionable fixes, not passive error alerts
Fix missing compliance evidence in seconds with in-ticket developer buttons—no compliance manuals or wiki pages required.
- 1-click: Append AC checklist template
- 1-click: Apply QA sign-off & verified label
5-Second Auditor CSV & PDF Export
Stop compiling messy spreadsheets for audit season. Download complete audit-ready workpapers with timestamps, reviewer handles, and commit SHAs.
- 1-click batch export for entire releases
- Clean CSV format auditors expect
Tamper-evident logs auditors can't dispute
Every resolved ticket locks an immutable SHA-256 fingerprint. If someone modifies a ticket retroactively, EvidenceLog flags the tampering immediately.
- Cryptographic proof stored in Jira KVS
- Auditors can verify offline on their own laptops
Vanta, Drata & Global Framework Ready
Satisfies US SOC 2 (CC8.1), ISO 27001 (A.8.32), European DORA, and Australian APRA CPS 234 change controls out of the box.
- Direct payload export for Vanta & Drata GRC
- 1-click printable SOC 2 verification certificate
Continuous change compliance sealed in Jira.
Free for squads up to 10 users. Zero external servers, no credit card required.
One automated engine. Every major audit standard.
Whether your auditor inspects for US SOC 2, ISO 27001, APRA CPS 234, or European DORA, the underlying engineering requirements are identical: peer review, test verification, and tamper-evident records.
SOC 2 Type II
Enforce Author ≠ Approver segregation of duties and lock automated change evidence for annual Big 4 audits.
ISO/IEC 27001:2022
Automate change management criteria, peer review verification, and rollback fallback procedures in-situ.
APRA CPS 234
100% Sydney data residency (ap-southeast-2) with zero data egress for Australian banks and fintechs.
DORA & UK FCA
Satisfy ICT operational resilience testing, rollback plans, and change audit trails directly inside Jira Cloud.
Zero Cross-Border Transfer. Data never leaves your Jira Cloud region.
EvidenceLog executes strictly within Atlassian microVMs and stores audit logs in your Jira tenant's encrypted Key-Value Storage (@forge/kvs). No foreign databases. No external telemetry. No material outsourcing delays.
PRICING
Simple, transparent pricing for every team
Billed conveniently through your standard Atlassian Cloud invoice. No separate credit card required.
Free Plan
Perfect for testing & squads up to 10 users
- Up to 10 Jira Cloud users
- Atlassian Forge native execution
- Automated PR review verification
- SHA-256 cryptographic seal
- Standard CSV workpaper export
Pro Growth
Continuous SOC 2 & ISO 27001 automation
- Unlimited Jira users & projects
- Separation of duties automatic check
- 1-Click SOC 2 & ISO 27001 Auditor Pack
- Vanta, Drata & Secureframe sync
- GitHub, GitLab & Bitbucket support
- Priority developer support
Enterprise
For multi-instance Jira & custom GRC SLAs
- Multi-instance Jira Cloud aggregation
- Custom compliance control mapping
- Dedicated compliance architect review
- Vendor security assessment support
- 99.9% uptime SLA & dedicated channel
Frequently asked questions
Essential answers for engineering leaders and compliance teams.
GitHub and GitLab enforce pull request reviews in Git, but auditors audit Jira. When your auditor asks for 40 random change samples from the last 12 months, your team has to manually cross-reference Jira tickets, open PRs, screenshot review timestamps, verify CI runs, and paste them into spreadsheets.
EvidenceLog eliminates that entire chore by locking the proof directly inside the Jira ticket at the moment of resolution. Read our deep dive on why branch protection fails audits